KVKK compliance in software means meeting the requirements of Law No. 6698 on the Protection of Personal Data (KVKK, Turkey's counterpart to the GDPR) not only through legal documents but through the design of the software itself. In practice, that means collecting only the data you need, informing users at the right moment, getting explicit consent where required, storing data securely, and building infrastructure that can handle deletion and access requests. This article isn't legal advice; it summarizes the key points product owners should know before development starts.
Key concepts
These are the concepts you'll run into most often in software projects:
- Personal data: Any information relating to an identified or identifiable natural person. Name, email, phone number, IP address, location and device identifiers can all fall under this.
- Special categories of personal data: More strictly protected types of data listed in the law, such as health, biometric data, religion and ethnic origin.
- Data controller: The party that determines the purposes and means of processing. As the product owner, that's usually you.
- Data processor: The party that processes data on behalf of the controller. Your hosting provider, email service, or the team that builds and maintains your software can be in this role.
- Explicit consent: Consent on a specific matter, based on information and given freely.
An important point: the law doesn't tie the processing of personal data to explicit consent alone. There are other legal grounds, such as performance of a contract, legal obligation or legitimate interest. Identifying which ground each processing activity relies on saves you from adding unnecessary consent checkboxes.
Design principles for KVKK compliance in software
Data minimization
You don't have to protect data you never collect. For every form field, ask "what do we need this for?" An age range may be enough instead of a date of birth, and a city instead of a full address. This is how the law's proportionality principle translates into software.
Purpose limitation
Using data you collected for one purpose for a different purpose may require a separate legal basis. For example, using a phone number collected for an order to send marketing messages requires separate approval. Your data model should include fields that can keep track of this distinction.
The duty to inform
When data is collected, users should be told the identity of the data controller, the purposes of processing, to whom and why the data may be transferred, the method and legal basis of collection, and their rights. In software, that means an accessible link to the privacy notice on sign-up and form screens.
Getting explicit consent right
For processing that requires explicit consent:
- The consent checkbox must not be pre-ticked.
- Consent must not be made a precondition of the service (unless it's genuinely necessary).
- Consent should be collected separately for different purposes.
- When consent was given, and for which version of the text, must be recorded.
- Users must be able to withdraw consent easily.
Retention and disposal
Each type of data should have a defined retention period, and when that period ends the data should be deleted, destroyed or anonymized. In software, that means automated deletion or anonymization jobs, with backups covered by the same policy.
Cookies, analytics and third-party scripts
In web apps, personal data is often collected unnoticed through third-party scripts: analytics tools, ad pixels, live chat widgets, embedded videos. Each of these can place cookies on the user's device and send data to servers abroad. For compliance, these points matter:
- Cookies and tracking tools that aren't essential for the app to work shouldn't load until the user consents.
- Cookie preferences should be saved, and users should be able to change them whenever they want.
- Keep a list of which third-party tool collects which data, and keep it consistent with your cookie policy.
- Update that list whenever a new tool is added; a marketing team adding a script without telling the developers is a common compliance gap.
Technical security measures
The law requires data controllers to take the technical and administrative measures needed to ensure an appropriate level of security. On the software side, the core measures are:
- Encryption in transit: All traffic should go over HTTPS.
- Protection at rest: Passwords should be hashed with strong one-way algorithms, and sensitive fields encrypted where necessary.
- Authorization: Users and employees should only be able to access the data they need for their work.
- Access logs: Record who did what to personal data, and when.
- Backup and restore: Back up regularly, encrypt the backups and test restoring them.
- No real data in test environments: Use anonymized or synthetic data in development and testing.
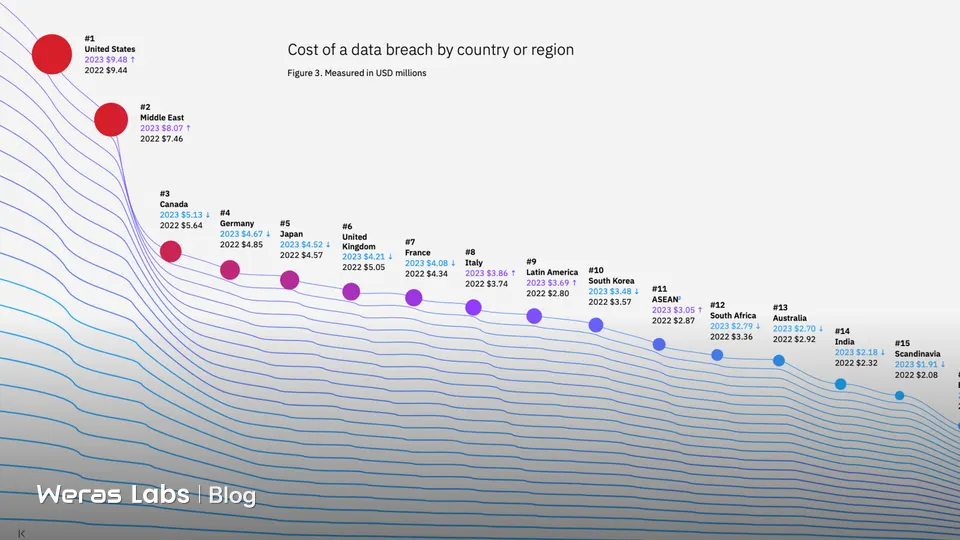
In the event of a data breach, there's an obligation to notify the Personal Data Protection Authority and the people affected. That's why monitoring and logging that can detect unusual access is also part of compliance.
Supporting user rights in your software
KVKK gives individuals rights such as learning whether their data is processed, requesting information, correction and deletion, and learning which third parties their data was transferred to. To respond to these requests on time, plan for the following in your software:
- Finding all of a user's data in one place,
- Exporting the data in a readable format,
- Deleting or anonymizing the account and related data,
- Separating records subject to legal retention obligations (such as invoice details) from the deletion process.
Services abroad and the GDPR
If your hosting, email, analytics or AI services are located abroad, this may count as a transfer of personal data abroad. The law's provisions on international transfers were updated by an amendment in 2024, and the mechanism the transfer relies on should be assessed separately.
If your product serves people in the European Union, the EU General Data Protection Regulation (GDPR) may apply as well. The GDPR's privacy by design approach overlaps heavily with the principles above.
Pre-development KVKK checklist
- All personal data collected, and its purposes, listed.
- Legal basis for each processing activity identified.
- Privacy notice prepared and linked from the relevant screens.
- Places requiring explicit consent designed with separate, unticked, logged checkboxes.
- Retention periods and an automated deletion or anonymization plan in place.
- Third-party services and data locations listed.
- Role-based authorization and access logs designed.
- Admin tools planned for deletion, export and correction requests.
- A review of obligations with a legal advisor scheduled.
Conclusion
KVKK compliance in software comes from design decisions made on day one, not from a privacy notice bolted on at the end. Collecting less data, separating purposes, layering security and planning tools to respond to user rights from the start prevent expensive fixes later. At Weras Labs, we go over personal data flows together with clients at the proposal stage; you can read about how we work on our services page. For your legal obligations, we strongly recommend getting an opinion from a legal advisor.
From Weras Labs
We can help you with this
We turn what you just read into working software for your business. You talk to the person writing the code; price and timeline are clear from day one.
Frequently asked questions
Does every piece of software need explicit consent?
No. Besides explicit consent, KVKK recognizes other legal grounds such as performance of a contract, legal obligation and legitimate interest. You need to identify the appropriate legal basis for each processing activity.
Is a privacy notice the same as an explicit consent form?
No. The privacy notice is the obligation to inform users about data processing, and it's required in every case. Explicit consent is a separate approval collected only for processing that relies on consent.
What role does a software agency play under KVKK?
If the agency accesses or processes personal data on your behalf, it's usually a data processor. In that case, it's important to spell out each party's obligations clearly in the contract.
Is using a cloud server abroad a violation of KVKK?
Not in itself, but it may count as transferring personal data abroad, so it has to rest on a mechanism that meets the law's transfer requirements. This assessment should be made together with a legal advisor.
About the author
Habip Dayan
Founder of Weras Labs
Habip Dayan is the founder of Weras Labs, a company that builds software products for professionals and teams. He has been building software since 2018 and writes about AI, cloud architecture and product design.
Comments
Be respectful; no ads or personal data. Comments that break the rules are removed.